The Critical Infrastructure Blind Spot in the AI Era

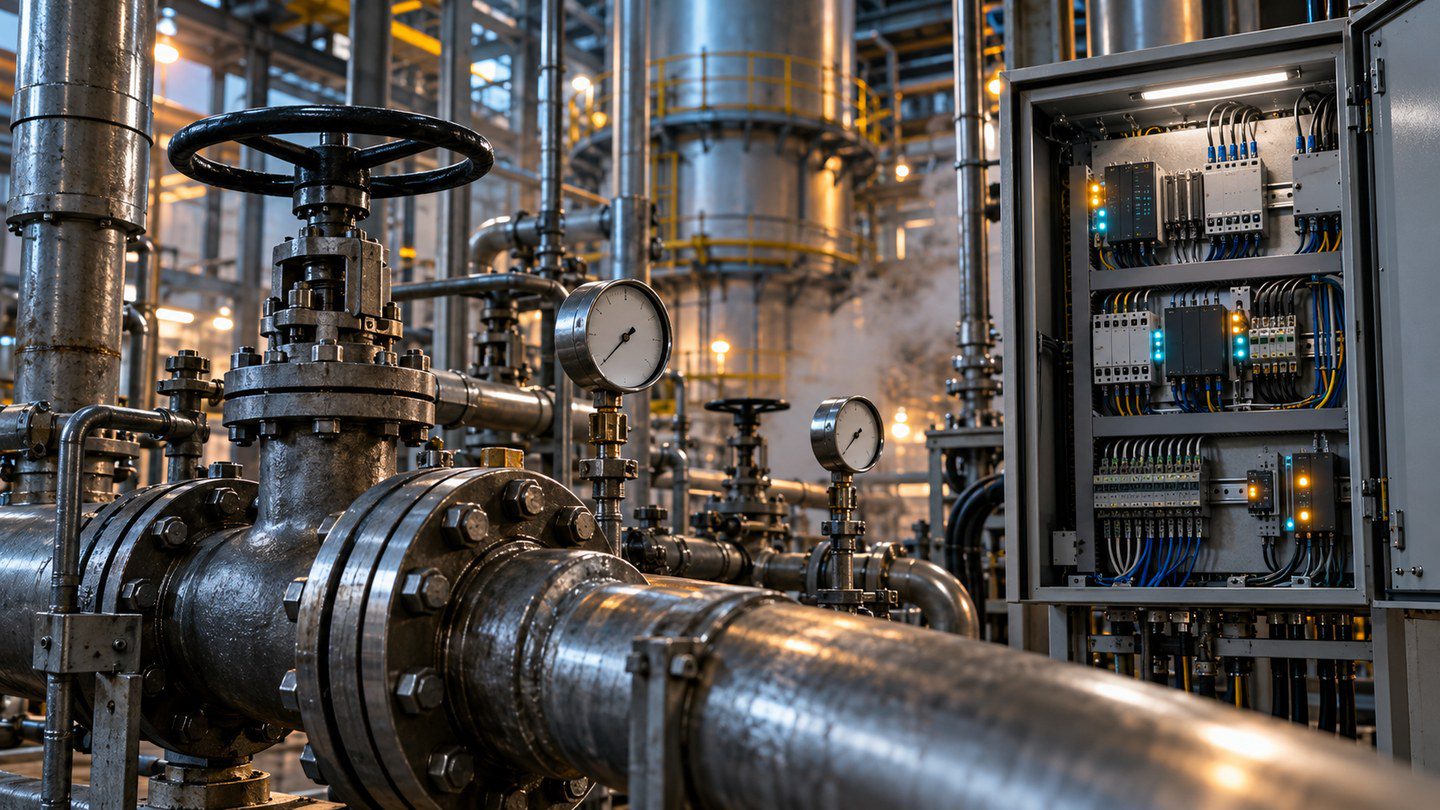
Reading cybersecurity solely through computer screens misses the physical reality and kinetic risk of critical infrastructure.
While deploying advanced artificial intelligence models for cybersecurity vulnerability discovery promises early defensive advantages, architecting defense solely around enterprise IT and cloud infrastructures leaves a massive blind spot across critical physical assets. An exploit in corporate IT typically leads to data exfiltration or temporary downtime, whereas an unmitigated vulnerability in operational technology, if safety instrumented layers are bypassed, can trigger uncontrolled valve releases, mechanical equipment damage, and direct threats to physical safety. This analysis examines why patching cycles in continuous 24/7 mission-critical operations span years rather than weeks, and why AI-assisted defense must place operational technology at the core of the table.
The Cybersecurity Illusion of AI Laboratories
Leading artificial intelligence research laboratories, including Anthropic and OpenAI, have begun granting controlled access to their advanced reasoning models to help select institutions discover security vulnerabilities ahead of adversaries. On paper, this strategy appears undeniably sound: arm defenders with proactive capabilities to identify and remediate weaknesses before malicious actors can exploit them.
Yet this initiative raises a fundamental engineering question: Which defenders are actually receiving this advantage?
Examining the roster of participating organizations reveals cloud hyperscalers, enterprise software conglomerates, web application security firms, and corporate IT operations sitting at the center of the table. In stark contrast, operational technology (OT) specialists who protect water treatment plants, high-voltage electrical grids, chemical synthesis reactors, railway interlocking hubs, and continuous manufacturing facilities are virtually absent.
Designing an AI-driven security ecosystem solely through an enterprise IT lens leaves the most fragile and physically consequential perimeter completely unshielded.
Physical and Kinetic Consequences of Cyber Vulnerabilities
In corporate information technology, the fallout from a successful intrusion remains largely contained within the digital boundary:
- A customer database may be exfiltrated,
- Email servers may suffer unauthorized access,
- A web application may experience several hours of outage,
- An enterprise may incur financial penalties or reputational damage.
While these consequences are substantial, a security breach in operational technology extends far beyond screen pixels. When physical process protections and safety interlocks are circumvented or manipulated, an operational exploit translates directly into kinetic danger:
- A high-pressure steam valve opened by a spoofed control command,
- A chemical batch reactor overheating because its cooling water loop was disabled,
- A municipal water treatment facility manipulated via SCADA to inject toxic concentrations of sodium hydroxide,
- An electrical generation turbine overspeeding until catastrophic centrifugal disintegration occurs,
- Railway signaling logic corrupted to display green aspects to converging passenger trains.
The real world does not run on server racks and relational databases alone. Pumps, valves, pressurized piping, steam turbines, programmable logic controllers (PLCs), and robotic manipulators form its physical backbone. Consequently, a vulnerability in operational systems does not represent abstract data loss; it directly threatens environmental contamination, structural destruction, and human life.
Security Philosophy: The Primacy of Safety and Availability
The inability to merge corporate IT and industrial OT into a uniform cybersecurity paradigm stems from a fundamental divergence in operating philosophy. Enterprise IT security is anchored in the classical triad of confidentiality, integrity, and availability:
- Confidentiality: Preventing unauthorized disclosure of sensitive data remains paramount.
- Integrity: Ensuring information is accurate and has not been tampered with.
- Availability: Maintaining system responsiveness when authorized users require access.
When suspicious traffic or anomalous exfiltration is detected in a corporate network, the IT team’s immediate, rational instinct is to sever network connections, isolate endpoints, and initiate reboots. In an office environment, sacrificing availability to protect confidentiality is an entirely justifiable tradeoff.
Across industrial infrastructure, that equation is reversed, with human safety taking absolute precedence:
- Human Safety: Preventing fatal injury to operating personnel and neighboring communities.
- Availability: Ensuring hard real-time, deterministic system execution 24 hours a day, 365 days a year.
- Integrity: Guaranteeing that pressure, temperature, and flow telemetry reflects physical truth.
- Confidentiality: Protecting internal data streams, subordinate to core physical functions.
In a continuous rotary kiln or a regional power dispatch substation, an operator cannot abruptly halt operations to inspect anomalous packets. An uncoordinated trip freezes molten material inside vessels, causes millions of dollars in mechanical destruction, or triggers cascading blackouts across regional grids.
Why Patches Cannot Be Deployed Immediately in the Field
One of the central promises of automated AI security tooling is the rapid generation and deployment of code patches. When a flaw is uncovered in enterprise software, remediations can be compiled, regression-tested in staging environments, and rolled out to production clusters within days or weeks.
In critical infrastructure, patching timelines span months and often years:
- Legacy and Extended Lifecycles: Enterprise IT hardware is routinely refreshed on three to five-year cycles. In contrast, field-deployed PLCs, remote terminal units (RTUs), and protective relays are engineered to deliver 20 to 30 years of uninterrupted service. Most of these field devices lack the memory capacity or compute power to run modern cryptographic handshakes or complex runtime agents.
- Risk of Compromising Determinism: In industrial automation, any software or firmware modification can alter scan times and interrupt cycles by microseconds. Before applying an update to operational hardware, engineering teams must validate the change over weeks within physical hardware-in-the-loop simulation facilities.
- Impossibility of Unplanned Downtime: Applying firmware patches typically requires power cycling field controllers. Major petroleum refineries, petrochemical complexes, and power plants schedule comprehensive maintenance turnarounds only once every two to four years.
Consequently, prescriptive guidance from AI models instructing teams to immediately apply code patches directly conflicts with field realities. For an automation engineer, true resilience is achieved not through continuous live patching, but via strict network segmentation, unidirectional data diodes, hardware-enforced microsegmentation, and rigorous IEC 62443 defense-in-depth architectures.
Architectural Boundaries of Critical Infrastructure Defense
To architect meaningful security across critical infrastructure in the AI era, engineers must clearly differentiate the operational boundaries governing both domains:
| Comparison Dimension | Enterprise IT | Critical Operational Technology (OT) |
|---|---|---|
| Core Priority Order | Confidentiality > Integrity > Availability | Human Safety > Availability > Integrity > Confidentiality |
| Worst-Case Scenario | Data breach, financial loss, reputational damage | Physical destruction, loss of life, environmental disaster, grid collapse |
| System Lifecycle | 3 to 5 years hardware and software refresh | 15 to 30 years continuous rugged field service |
| Patch and Update Frequency | Daily or weekly automated reboots | Annual planned maintenance turnarounds, extended bench testing |
| Component Types | Servers, databases, operating systems, endpoints | PLCs, SCADA software, RTUs, sensors, valves, pumps |
| Determinism Requirement | Latency tolerated (seconds) | Hard real-time deterministic response (milliseconds) |
| Primary Defense Strategy | Endpoint protection, identity verification, rapid patching | Network segmentation, IEC 62443 defense-in-depth, isolated tunnels |
A Security Approach Blind to the Field is Dangerous
The analytical speed and pattern recognition capabilities that frontier AI models bring to vulnerability research represent a genuine technical milestone. However, an algorithmic model identifying a heap buffer overflow in a C codebase cannot, on its own, prevent an industrial furnace from exploding.
Artificial intelligence does not intrinsically possess field awareness:
- It cannot deduce the physical pressure tolerance of a downstream gate valve linked to a specific ladder logic routine,
- It cannot predict whether a millisecond delay in a PROFINET or Modbus TCP frame will inadvertently trip a safety instrumented system,
- It cannot assess how a software change might destabilize cross-coupled interlocks on an active assembly line.
If advanced AI models are to genuinely empower defenders, security initiatives cannot remain confined to corporate data centers and web interfaces. Operational technology cybersecurity practitioners, control systems architects, and field engineers must hold permanent seats at the decision table.
A security strategy that fails to account for physical valves, steam turbines, and emergency shutdown interlocks is not merely incomplete; by fostering an illusion of safety, it is actively dangerous.
📚 References
CISA (2023). Cross-Sector Cybersecurity Performance Goals for Critical Infrastructure. Cybersecurity and Infrastructure Security Agency Technical Report.
IEC (2018). IEC 62443: Security for Industrial Automation and Control Systems. International Electrotechnical Commission Standard Series.
SANS Institute (2024). SANS State of ICS/OT Cybersecurity Survey: Addressing the Real-World Attack Surface. SANS Research.
OpenAI (2023). OpenAI Cybersecurity Grant Program: Advancing AI-Assisted Cyber Defense. OpenAI Technical Initiatives.
Anthropic (2024). Frontier Red Teaming and Vulnerability Discovery in Software Security. Anthropic Research.
📋 Related Links
🔗 Hardware Architecture to Overcome the IT/OT Barrier: Secure Remote Service for Machine Builders
📂 Blog: Technology and Systems Articles
📄 Turning Dark Data in the Field into Value with IIoT Infrastructure